Cleared for Takeoff? How Threats Can Slip Into Your Salesforce Orgs Through Files, Links, and AI Agents
Salesforce threat scanning explained: how files and links enter through Experience Cloud, Email-to-Case, and APIs.

Salesforce threat scanning explained: how files and links enter through Experience Cloud, Email-to-Case, and APIs.
Connect Claude to Salesforce without exposing your org. Learn the risks to fix first, from read-only servers to External Client App controls.

Vet open source tools for Salesforce security before they reach production. Nicolas Vuillamy shares the checks that keep your org safe.
Salesforce Profile Filtering can silently break automation in Winter 27. Learn 5 technical fixes for Apex, validation rules, and SOAP login.
Salesforce MCP security with Mike Rogan on what Claude can access, why read-only servers come first, and how to audit agent activity.
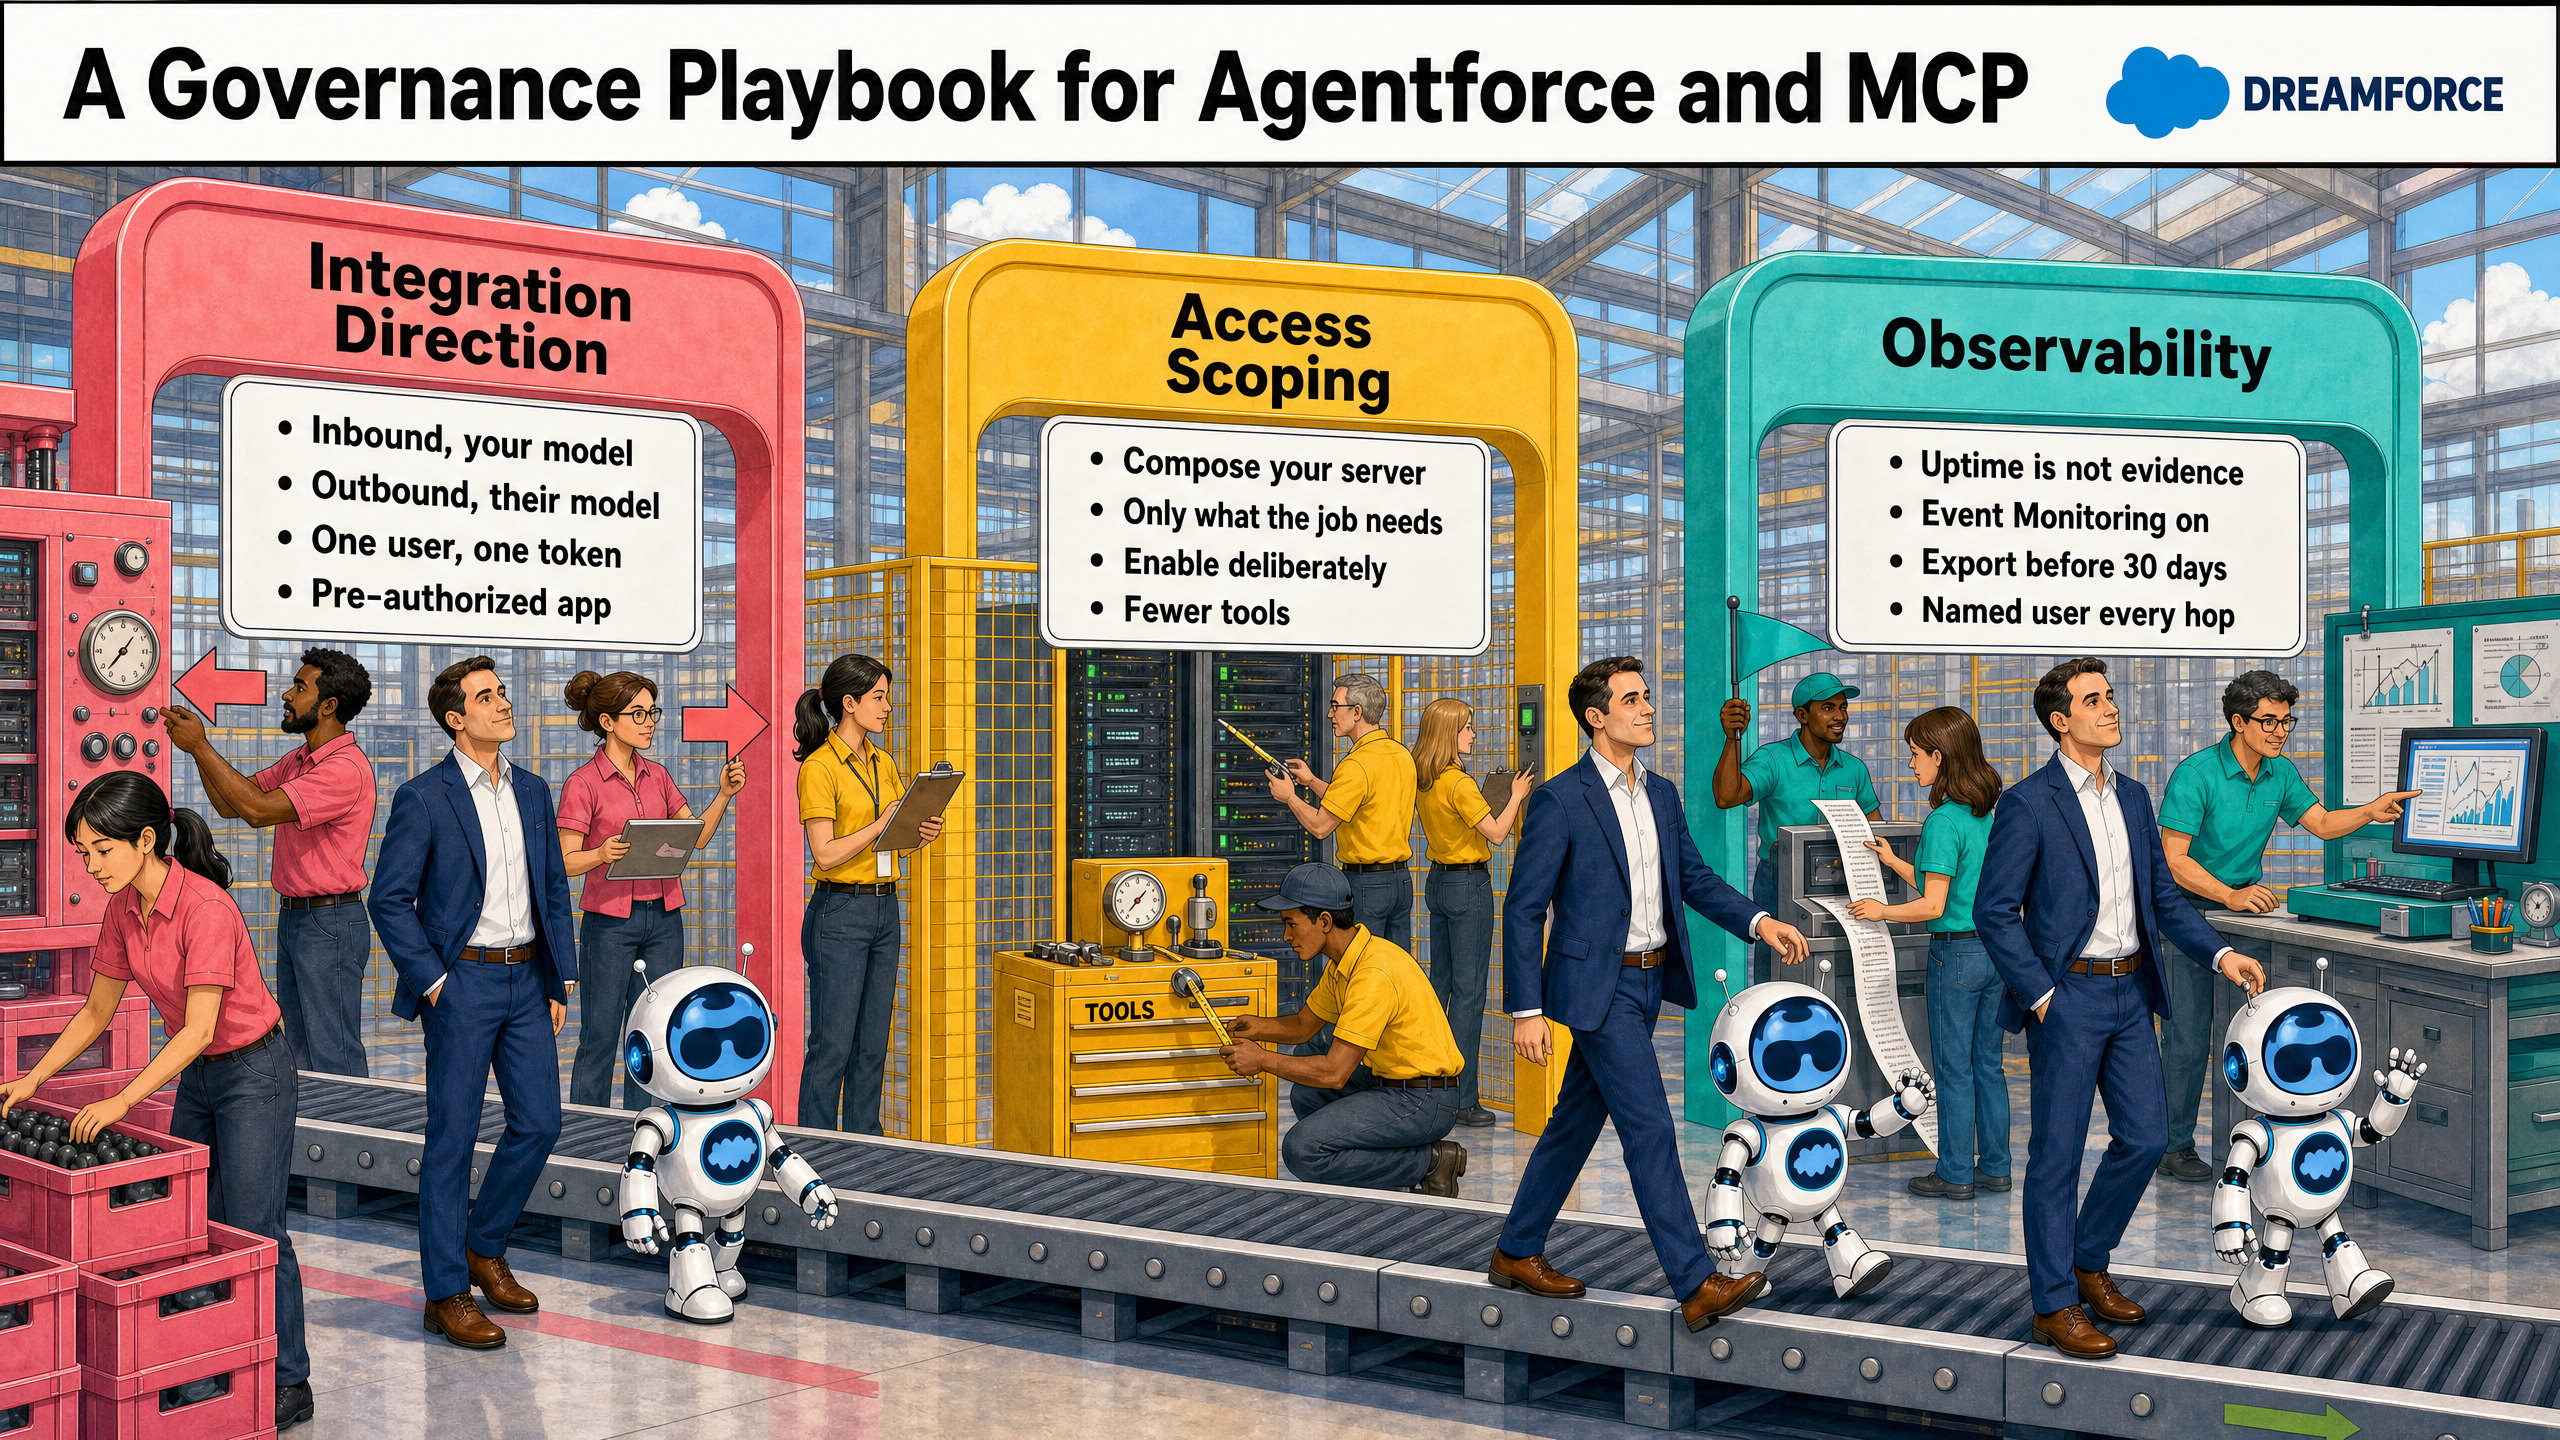
Watch the Dreamforce 2026 session on Agentforce MCP governance, covering trust boundaries, observability, and secure agent orchestration.
Salesforce Winter 27 Profile Filtering explained. Saman Attar shows how to find and fix Apex and validation rule references. Demo included.
Salesforce malware scanning is on by default, but files over 100 MB, legacy attachments, and older uploads still reach your org unscanned.
Geraint Waters on how AI agents expose Salesforce data, what native testing misses, and how to build an OWASP-based test plan before go-live.

Microsoft mapped a year of Salesforce breaches at 1,000+ orgs. The 10 fixes security leaders need to act on.